
Cybersecurity
How to Tell if a Browser Extension Is Safe Before You Install It: A Practical Guide to Spotting Fake Productivity, Coupon, and AI Add-ons That Can Read Your Data
LinkExpln Team · Published November 5, 2026
Browser extensions can save time, fill forms, summarize pages, compare prices, and add AI tools to your browser. But they can also request broad access such as reading page content, changing what you see, or collecting browsing activity. That does not automatically mean an extension is malicious, but it does mean you should check it carefully before installing it.
Key takeaway: Treat browser extensions like apps with powerful permissions. Before you install one, check who made it, what permissions it asks for, whether the listing and reviews look genuine, and whether you really need it. If you are unsure, test the link or site first with the LinkExpln scanner and install only from the browser’s official extension store.
Why browser extensions can be risky
A browser extension runs inside your browser, which is where you log in, shop, read email, and enter sensitive information. Depending on its permissions, an extension may be able to read page content, change webpages, access tabs, or communicate with remote servers. Google’s Chrome extension permission guidance explains that permissions should be reviewed carefully because they affect what an extension can access and do (Google Support). Mozilla also advises users to review requested permissions and install extensions only from trusted sources (Mozilla Support).
This matters because fake “productivity,” “coupon,” and “AI assistant” extensions often promise something useful while quietly asking for more access than their function reasonably needs. A coupon finder may want to “read and change all your data on all websites.” An AI sidebar may ask to access every page you visit. Sometimes that access is needed for core features, but sometimes it is excessive.
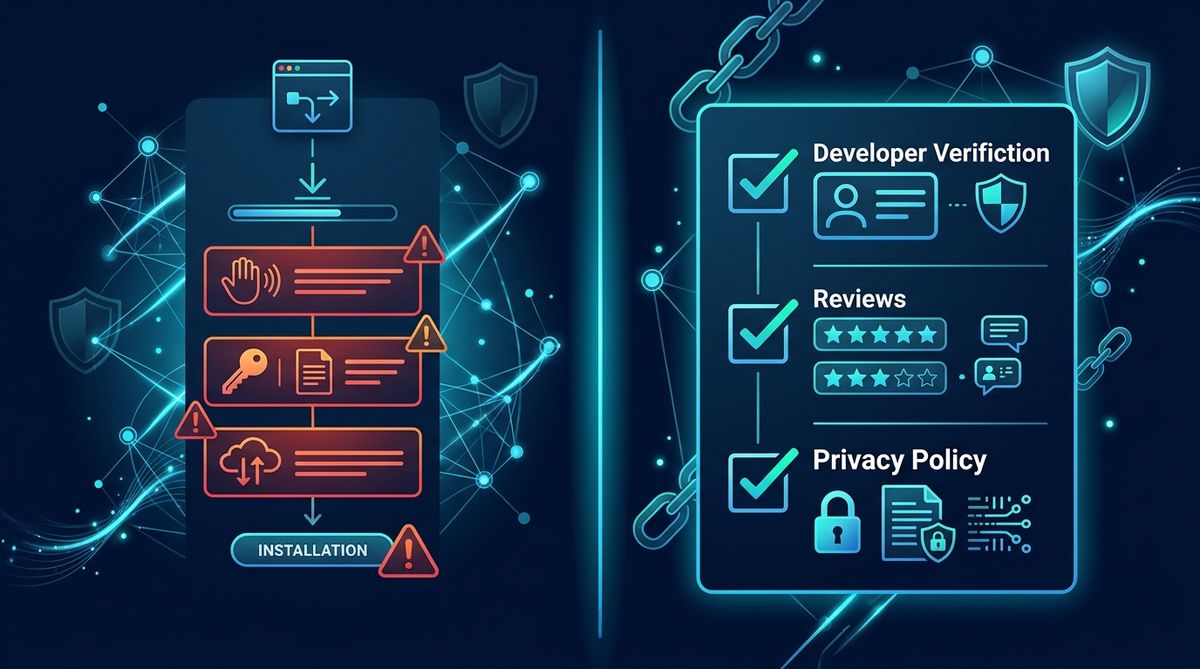 Illustrative image (AI-generated).
The safest way to install an extension
1. Use the official browser store only
Install extensions only from the official store for your browser, such as the Chrome Web Store or Firefox Add-ons. Avoid downloads from random websites, forum posts, or ads that tell you to “manually install” a file. Browser makers and government agencies consistently warn users to get software and add-ons from official sources where possible, because that reduces the chance of tampering or impersonation (CISA).
If a website pushes you to install an extension directly and creates urgency like “required to continue” or “your video cannot play without this tool,” leave the page.
2. Search for the developer outside the extension listing
A polished store page is not enough. Click the developer name and look for:
- An official website with clear contact details
- A privacy policy that explains what data is collected
- A support page or documentation
- A recognizable company, project, or publisher identity
If the extension claims to be from a known service, verify it from that service’s main website rather than trusting the store listing. Impersonation is common in scams: a fake add-on can copy logos, screenshots, and branding to look legitimate.
How to check whether the permissions make sense
Permissions are one of the best clues.
Common permission red flags
Be cautious if an extension asks for:
- Access to all websites when its feature should work only on one or two sites
- Read and change your data on all websites for a simple tool like a calculator, wallpaper, or basic coupon alert
- Access to browsing history or tabs without a clear reason
- Clipboard access if the feature does not obviously need it
- Downloads or file access for a tool that only claims to summarize text or generate prompts
Google notes that permissions tell you what the extension can do, and users should review them before installation (Google Support).
When broad permissions may be legitimate
Some extensions genuinely need wide access. Examples include password managers, ad blockers, accessibility tools, and page translators. The question is not “Does it ask for powerful access?” but “Does that access clearly match the feature?”
If the answer is unclear, do not install it yet. Read the help documentation, search for independent discussions, or choose a better-known alternative.
Spotting fake productivity, coupon, and AI add-ons
These categories are popular because they are easy to market and can attract lots of installs.
Warning signs on the extension listing
Look out for:
- Overhyped claims like “instant money saving on every site” or “AI for every page, 100% private” with little detail
- Poor grammar, inconsistent branding, or mismatched screenshots
- Very few reviews despite very high claimed usefulness
- Many short, generic reviews such as “Great app,” “Best extension,” or repeated phrases that look copied
- Recent review spikes after a long quiet period
- No meaningful update notes or a very new developer account
- A privacy policy that is vague, missing, or copied from somewhere else
Extra caution for coupon extensions
Coupon and cashback tools may legitimately need to know which shopping site you are on. But if they ask for access across all browsing, check whether that is explained clearly. The U.S. Federal Trade Commission advises consumers to be careful with shopping tools, privacy practices, and claims that seem too good to be true (FTC Consumer Advice).
Extra caution for AI extensions
AI add-ons often ask to read current page content so they can summarize or answer questions. That may be expected. But if the extension also wants broad background access, requests login tokens, or gives no explanation of where your data goes, think twice. Sensitive pages such as webmail, banking, internal work systems, and legal documents should be treated with extra care.
A practical step-by-step check before installing
Step 1: Ask whether you really need the extension
Can you do the same thing using a website, a built-in browser feature, or a trusted standalone app? Fewer extensions usually means lower risk.
Step 2: Verify the source
Find the extension through the official store and cross-check the developer on its official website.
Step 3: Read the permissions carefully
Do not skip the install prompt. Ask: does each permission fit the advertised function?
Step 4: Review the privacy policy
Look for plain-language answers to these questions:
- What data is collected?
- Is page content sent to remote servers?
- Is data sold or shared for advertising?
- Can you delete your data?
Step 5: Check reviews for patterns, not just star ratings
Read low-star and mid-star reviews. They often reveal problems with pop-ups, unexpected redirects, broken updates, or unexplained data access.
Step 6: Search for outside mentions
Look for the developer’s documentation, GitHub repository if relevant, media coverage, or discussions in established communities. No outside footprint is not proof of danger, but it is a reason to be more cautious.
Step 7: Test the site or install page if something feels off
If you reached the extension through a link in an ad, message, or random website, scan that URL with the LinkExpln scanner or report a suspicious link if you think others may be targeted.
What to do after installation
Installing carefully helps, but you should still limit risk.
Good habits after you install
- Review extension permissions periodically
- Disable or remove extensions you no longer use
- Keep your browser updated
- Avoid using unnecessary extensions on work, banking, or email accounts
- Check whether the extension suddenly changed owner, branding, or behavior after an update
CISA recommends updating software and using strong security habits to reduce exposure to threats (CISA).
If an extension starts opening new tabs, injecting ads, changing search settings, or asking you to log in again on multiple sites, remove it immediately and run a browser security check. You can also review broader security practices to reduce account and device risk.
Illustrative example
Illustrative example: “Install this AI study helper to summarize every site. Works instantly on Gmail, banking, and all school portals. Click Allow on all permissions to continue.”
Why this is risky:
- It pressures you to act quickly
- It normalizes access to sensitive sites
- It asks for broad permissions without explaining why
- It frames full access as mandatory rather than optional
FAQ
Is every extension that asks for broad permissions unsafe?
No. Some useful tools genuinely need broad access. The key question is whether the permissions are clearly necessary for the advertised feature.
Are official browser stores completely risk-free?
No. Official stores are safer than random downloads, but they are not a guarantee. You should still review the developer, permissions, and privacy policy.
Should I avoid AI browser extensions completely?
Not necessarily. Some are legitimate, but they may process page content in ways you should understand first. Be especially careful on email, finance, health, and work-related sites.
Conclusion
A safe browser extension should be easy to understand before you install it: who made it, what it does, what data it can access, and why. If the developer is hard to verify, the permissions seem excessive, or the listing feels manipulated, skip it and look for an alternative. Your next step: audit the extensions already in your browser today and remove any you do not fully recognize or need.
Stay Protected
Not sure about a link you received? Check it with the LinkExpln scanner or learn how LinkExpln works.
More articles